Understanding the Structure of the Data Security Policy
You can create a data security policy using the XS_DATA_SECURITY.CREATE_POLICY PL/SQL procedure.
Real Application Security Data Security Policy Created on the EMPLOYEES Table shows the structure of a Real Application Security data security policy named HR.EMPLOYEES_DS that is created from a data realm constraint and a column constraint, both of which are to be applied to the EMPLOYEES table. The data realm constraint defines the rows (DEPARTMENT_ID with a value of 60 or 100) on which the data security policy applies and the ACL (HRACL) that is associated with these rows. The column constraint defines a constraint for the sensitive column data in the SALARY column of the EMPLOYEES table by using the VIEW_SENSITIVE_INFO privilege that is required to view this sensitive data.
Real Application Security Data Security Policy Created on the EMPLOYEES Table
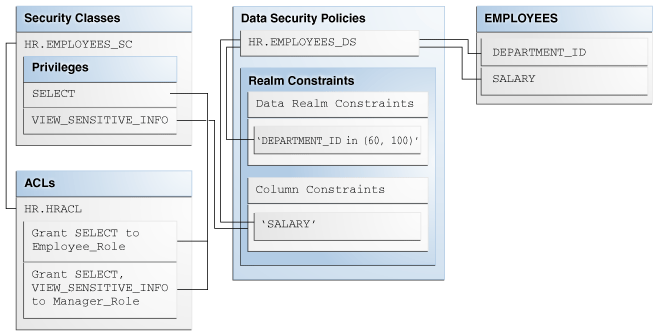
Description of the illustration dspolicy_emp.png
Example: Structure of a Data Security Policy creates the data security policy shown in Real Application Security Data Security Policy Created on the EMPLOYEES Table.
See Also: “CREATE_POLICY Procedure”
You should validate the data security policy after you create it. See “VALIDATE_DATA_SECURITY Function” for more information.
The main parameters of a data security policy are as follows:
-
Policy Name: This defines the name of the data security policy.
Example: Structure of a Data Security Policy uses the name
EMPLOYEES_DSfor the data security policy that it creates. -
Data Realm Constraints: The data realm constraints define the data realms, or the rows, on which the data security policy applies, together with the ACLs to be associated with these data realms.
Example: Structure of a Data Security Policy uses the
realm_conslist to define the data realm constraint for theEMPLOYEES_DSpolicy.realm_conscomprises of rows that have aDEPARTMENT_IDvalue of60or100. These rows are associated with theHRACLaccess control list. -
Column Constraint: Column constraint defines additional constraint for sensitive column data in the data realm constraint.
Example: Structure of a Data Security Policy associates the column_cons column constraint with the
EMPLOYEES_DSpolicy.column_consprotects theSALARYcolumn with theVIEW_SENSITIVE_INFOprivilege.
Example: Structure of a Data Security Policy
-- Create the ACL HRACL.
DECLARE
ace_list XS$ACE_LIST;
BEGIN
ace_list := XS$ACE_LIST(
XS$ACE_TYPE(privilege_list => XS$NAME_LIST('SELECT'),
granted => true,principal_name => 'Employee_Role'),
XS$ACE_TYPE(privilege_list => XS$NAME_LIST('SELECT', 'VIEW_SENSITIVE_INFO'), granted => true, principal_name => 'Manager_Role'));

sys.xs_acl.create_acl(name => 'HRACL',ace_list => ace_list, sec_class => 'HR.EMPOLYEES_SC');
END;

-- Create variables to store the data realm constraints and the column constraint.
DECLARE
  realm_cons XS$REALM_CONSTRAINT_LIST;
BEGIN

-- Create a data realm constraint comprising of a data realm (rule) and
-- an associated ACL.
  realm_cons :=
    XS$REALM_CONSTRAINT_LIST(
      XS$REALM_CONSTRAINT_TYPE(realm=> 'DEPARTMENT_ID in (60, 100)',
                               acl_list=> XS$NAME_LIST('HRACL')));

-- Create the column constraint.
  column_cons :=
    XS$COLUMN_CONSTRAINT_LIST(
      XS$COLUMN_CONSTRAINT_TYPE(column_list=> XS$LIST('SALARY'),
                            privilege=> 'VIEW_SENSITIVE_INFO'));

 -- Create the data security policy.
  SYS.XS_DATA_SECURITY.CREATE_POLICY(
          name=>'HR.EMPLOYEES_DS',
          realm_constraint_list=>realm_cons,
          column_constraint_list=>column_cons);

-- Enforce the data security policy to protect READ access of the EMPLOYEES table
-- and restrict access to the SALARY column using the VIEW_SENSITIVE_INFO
-- privilege.
  sys.xs_data_security.apply_object_policy(
           policy => 'HR.EMPLOYEES_DS',
           schema => 'HR',
           object => 'EMPLOYEES',
           statement_types => 'SELECT',
           owner_bypass => true);

END;